Data exclusively in the European Union, run by an ISO/IEC 27001 operator
The application runs in two data centres in the European Union, in Warsaw and Frankfurt. Every change passes automated tests and code review, the infrastructure is maintained by the operator’s DevOps team, and report content can be encrypted with the client’s key. No data leaves the Union.
Who maintains the system and how changes go in
sygnadesk is backed by software engineers and a DevOps team. The code, the infrastructure and every change are tested and monitored, before and after they reach you.
-
Rigorous testing of every update
A change reaches production after 1,064 automated tests, end-to-end tests and code review by a second person.
-
Red team and blue team checks
We regularly attack our own system (red team) and verify the defences (blue team) to catch gaps before anyone outside does.
-
DevOps and server security
DevOps engineers harden the servers and keep them available, patched, redundant and recoverable.
-
WAF and anti-DDoS protection
A web application firewall (WAF) and DDoS protection filter malicious traffic before it reaches the system.
-
24-hour monitoring
Round-the-clock monitoring of availability and security events with alerts to the operator’s on-call team.
-
Confidentiality built into the architecture
In end-to-end mode, report content and identity are encrypted with a key that stays with the client. Even the team maintaining the system cannot read a report, and if the organisation loses all its keys, nobody can recover the content.
-
Account and sessions under control
2FA for every role, recovery codes, a list of active sessions with logout, login history, an alert on a new device and automatic sign-out after 30 minutes. The operator panel works only from trusted addresses and does not allow impersonating another account.
-
Attachments checked before saving
Every file goes through an antivirus scan, and when the scanner does not respond, the file is rejected. Attachments are encrypted on disk, and metadata is removed from images, Office documents and recordings.
Who is the data controller
The first question any data protection officer asks. The answer is split, and it does not change with the plan you buy.
- Report content and reporter identity
- Your organisation remains the controller. sygnadesk acts as a processor under a data processing agreement and, in end-to-end mode, cannot read report content or the reporter’s identity.
- Account, contact details, billing
- The operator is the controller, to the extent needed to run the service. The privacy policy sets out the detail and the legal bases.
Data processing agreement, full text List of sub-processors, who we share processing with

Data centres in the European Union
Two EU locations provide performance and continuity. Reporter data is never transferred outside the European Economic Area.
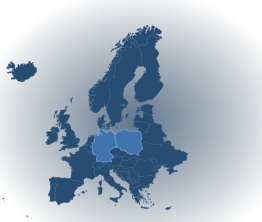
- Warsaw (PL)
- Frankfurt (DE)
- EU data only
-
Warsaw and Frankfurt
Two data centres in the European Union. Business continuity and low latency for users in the region.
-
24/7 physical security
Round-the-clock surveillance, access control and facility monitoring. Only authorised people reach the servers.
-
ISO/IEC 27001 certified
The system operator runs an information security management system compliant with ISO/IEC 27001.
-
Encryption in transit and at rest
TLS 1.3 on the wire and encrypted disks in the data centre. On top of that, report content and the reporter’s identity can be encrypted at the application layer with the client’s key (end-to-end mode).
-
EU data only
Hosting, backups and processing in the European Union. No transfer outside the European Economic Area.
-
Backups and monitoring
Regular encrypted backups, availability monitoring and a web application firewall (WAF) against attacks.
From the reporter’s browser to a data centre in the EU
The reporting page and the handling panel sit behind an edge network. Its node handles the connection and filters traffic, but stores no report content: every request for data goes to a data centre in the European Union.
-
The reporter’s browser
A TLS 1.3 connection to the nearest edge node. The reporting page loads no resources from external domains, so apart from this single connection no trace is created.
-
Edge node: a filter, not a store
The web application firewall (WAF) and DDoS protection inspect the request and pass it on. The node may cache only the application’s static files (stylesheets, fonts). It does not store report content or personal data.
-
Data centre in the European Union
This is where the data is: Warsaw and Frankfurt, encryption at rest, backups inside the EEA. In end-to-end mode, report content and identity are additionally encrypted with the client’s key.
Only the application’s static assets are cached at the edge. Report content and personal data are neither cached nor stored outside the data centre.

Certified data centres under constant guard
sygnadesk servers run in certified data centres in Warsaw and Frankfurt: round-the-clock surveillance and access control, power and cooling redundancy, fire protection and monitoring. Data never leaves the European Union.
- 24/7 physical security
- ISO/IEC 27001 certified
- EU data only
System operator
The owner and operator of the sygnadesk platform is:
Jeton Cloud spółka z ograniczoną odpowiedzialnością spółka komandytowa
Certificate number: 4801270
- VAT ID
- 5213901362
- KRS
- 0000850403
- REGON
- 386529721
- Address
- Domaniewska 37, 02-672 Warsaw, Poland
- Phone
- +48 22 378 48 62
- Contact
- hello@sygnadesk.com
Questions about security or compliance?
We are happy to answer questions from IT, security or compliance teams, and can share documentation on request.